CISA Flags Exploited Adobe Commerce Flaw as Stores Urged to Patch
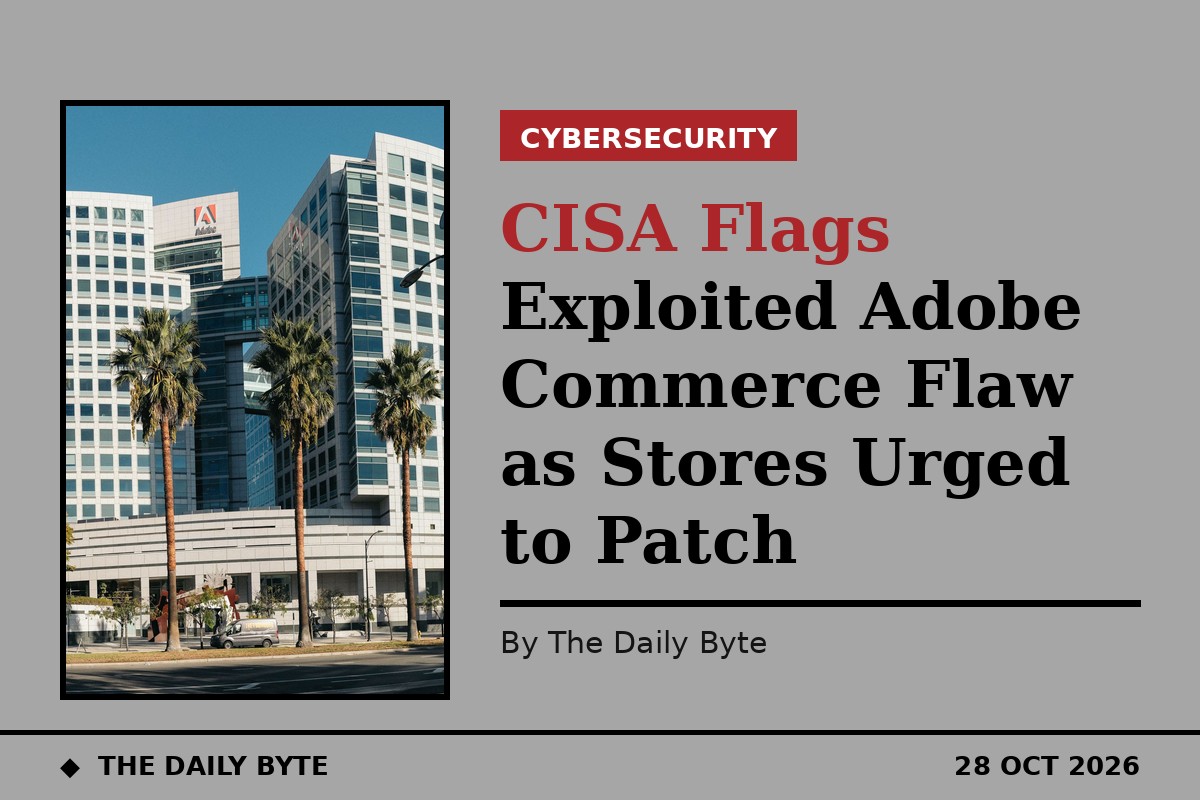
The US Cybersecurity and Infrastructure Security Agency has added a critical flaw in Adobe Commerce and Magento Open Source to its Known Exploited Vulnerabilities catalogue, confirming that attackers are actively using it. The entry, made on 27 October 2026, covers CVE-2026-48356 and sets 10 November 2026 as the remediation deadline for US federal civilian agencies. The listing is also a clear warning to private online stores, because inclusion in the catalogue is based on evidence of exploitation in the real world, not on a theoretical risk.
What the flaw allows
The weakness is an unrestricted upload of a file with a dangerous type, which can lead to arbitrary code running in the context of the current user. In practical terms, a store that is still running an unpatched version could be taken over through its file-upload handling, giving an attacker control over the affected account or session. Adobe's own record notes that exploitation requires user interaction, such as a victim visiting a maliciously crafted web address or interacting with a compromised page. CISA has not identified the attackers behind the exploitation, and it records ransomware involvement as unknown.
Why stores are still at risk
This is not a new flaw waiting for a fix. Adobe addressed it in July 2026 under bulletin APSB26-73, with corrected builds marked 2026-jul for the supported Adobe Commerce, Commerce B2B and Magento Open Source release lines, including Commerce 2.4.9 and earlier supported versions and Magento Open Source 2.4.9 and earlier. The October catalogue entry therefore points to a patching gap rather than a missing patch: stores that never applied the July update remain exposed months later, even though the corrected software has been available. The same 27 October catalogue update also added a Google Brotli compression-library flaw, CVE-2026-111497, with the same 10 November deadline.
What store owners should do
Store owners should install the matching 2026-jul build for their exact release line without delay, rather than assuming a general update has covered it. After patching, they should check upload folders, administrator accounts and content blocks or pages for signs of tampering, since a file-upload flaw can leave hidden code behind. If any sign of compromise is found, database, administrator and integration credentials should be rotated and the incident investigated, following vendor guidance. Discontinuing use of an unpatched product is the fallback where no fix is available, but for this flaw the fix already exists.