Critical LXD Flaw Lets Attackers Pose as Trusted Clients
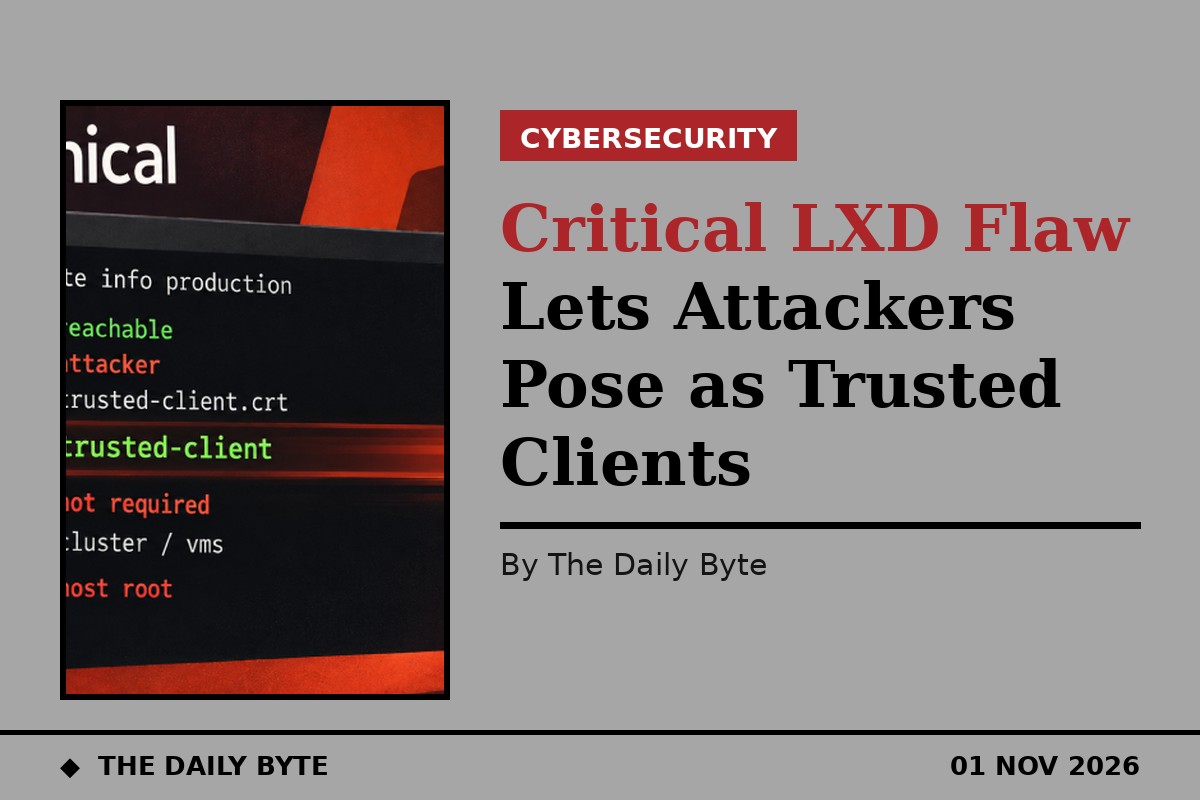
A critical flaw in Canonical's LXD and MicroCloud could let an attacker log in as a trusted client without holding that client's private key, according to reporting published on 1 November 2026. Tracked as CVE-2026-112816, it carries the maximum CVSS score of 10.0.
How the impersonation worked
LXD and MicroCloud let remote clients reach their interfaces over mutual TLS, using client certificates. A client counts as trusted when its certificate sits in the server's trust store. The flaw was in how the server checked certificates: it compared every certificate sent against the trust store, even though TLS only proves ownership of the private key for the first certificate in the chain. An attacker could therefore attach a trusted client's public certificate, which is not secret, behind their own and be accepted as that client.
Who was exposed, and what to do
Exploitation required network access to the HTTPS API and the public certificate of an already-trusted client. A standalone LXD server does not expose that API by default. MicroCloud cluster joining is a weak point: capturing a member's public certificate as it joins can allow login as that member. Affected LXD versions are 4.0.14, 5.0.10, 5.21.8 and 6.9. Canonical lists fixed snap versions LXD 6.10.1, 5.21.9, 5.0.11 and 4.0.15, and MicroCloud 3.4.1 and 2.1.5. Incus, which originally reported the flaw, fixed it in version 7.6.0. There is no public sign of exploitation: a US CISA assessment dated 30 October states it is not known to have been exploited, it is not on CISA's Known Exploited Vulnerabilities list, and no working exploit has been published, according to The Hacker News. Canonical advised updating, then checking the installed version, and limiting API network access until then.