CVE-2026-129444: Critical D-Link DSL-6740C Router Flaw Scores 9.3 Out of 10
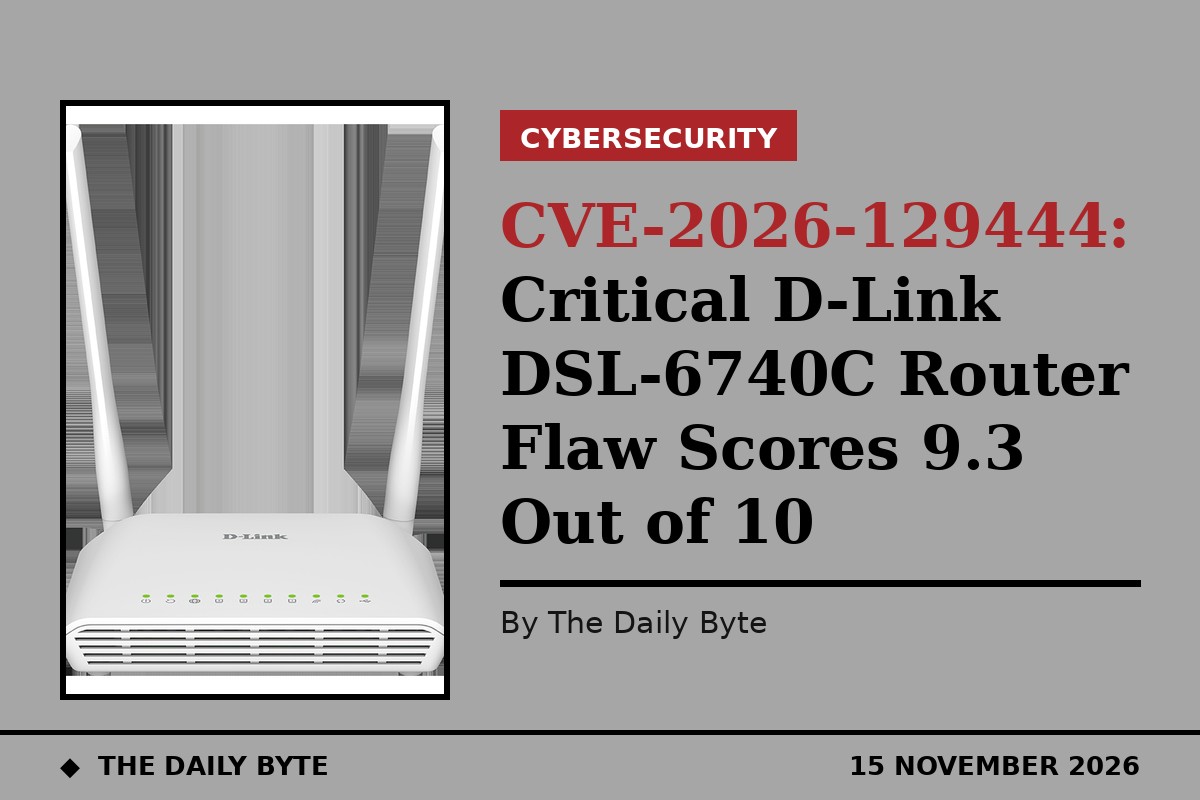
A critical security flaw has been disclosed in D-Link's DSL-6740C router, carrying a severity score of 9.3 out of 10. Tracked as CVE-2026-129444, the vulnerability was published on 15 November 2026 and centres on hard-coded credentials in the device's FTP service, which an attacker can abuse remotely without any login.
The flaw affects the DSL-6740C running firmware version 20131126. According to the National Vulnerability Database (NVD), the problem lies in the file /etc/templates/ftpd/ftpd_conf.php, part of the router's FTP daemon. Manipulation of that function exposes hard-coded credentials, giving an attacker a way into the device without needing to guess or crack a password.
Because the credentials are baked into the firmware, there is nothing for the owner to change: anyone who can reach the vulnerable function can use the same fixed login details. The CVE record states that an exploit for the flaw is publicly available, which lowers the barrier for opportunistic attackers and automated scanning tools.
Why the flaw is rated critical
The vulnerability scores 9.3 under CVSS version 4.0, placing it in the critical range. The score was assigned by VulDB, the CNA that published the record; the NVD had not yet issued its own assessment at the time of writing. The scoring vector shows the attack can be carried out over the network, needs no privileges and no user interaction, and can affect the confidentiality, integrity and availability of the device.
The flaw is classified under two related weaknesses: CWE-259, use of a hard-coded password, and CWE-798, use of hard-coded credentials. Both describe software that ships with fixed authentication data that users and administrators cannot change.
The DSL-6740C is a residential gateway, the kind of device that sits between a home or small business network and the internet. A compromised gateway can expose files stored on the device, allow configuration changes that redirect traffic, or serve as a foothold for moving deeper into the network behind it. VulDB's analysis warns that attackers could also use the access to install persistent backdoors for long-term surveillance or command and control.
No CISA warning yet
As of publication, the flaw has not been added to the US Cybersecurity and Infrastructure Security Agency's Known Exploited Vulnerabilities catalogue, which lists flaws confirmed as exploited in the wild. That does not mean the device is safe: the public availability of exploit code means attacks could begin at any time, and the catalogue only records exploitation once it has been confirmed.
The CVE record's references point to the researcher's evidence on GitHub and to D-Link's own website, but list no vendor security advisory or patch for this specific flaw. Owners should check D-Link's support pages for their model and apply any firmware update that appears.
What DSL-6740C owners should do
First, check whether you run a DSL-6740C on the affected firmware. If the router's FTP service is not needed, disable it: every unnecessary service is an extra way in. If FTP must stay on, make sure the device's management interfaces are not reachable from the internet, and use firewall rules or network segmentation to limit access to trusted devices only.
Owners should also watch for unusual login attempts or unexpected outbound traffic from the router, which can be early signs of compromise. Where a firmware update is available, install it promptly. If no update is offered for this older model, the safest step is to retire the device and replace it with a supported router that still receives security updates.
Hard-coded credentials remain one of the oldest problems in connected devices, and this disclosure is a reminder that routers which have not been updated for years can still be a live risk on a home network.
Sources: National Vulnerability Database; VulDB.


