CVE-2026-58115: Siemens Node-RED flaw under attack
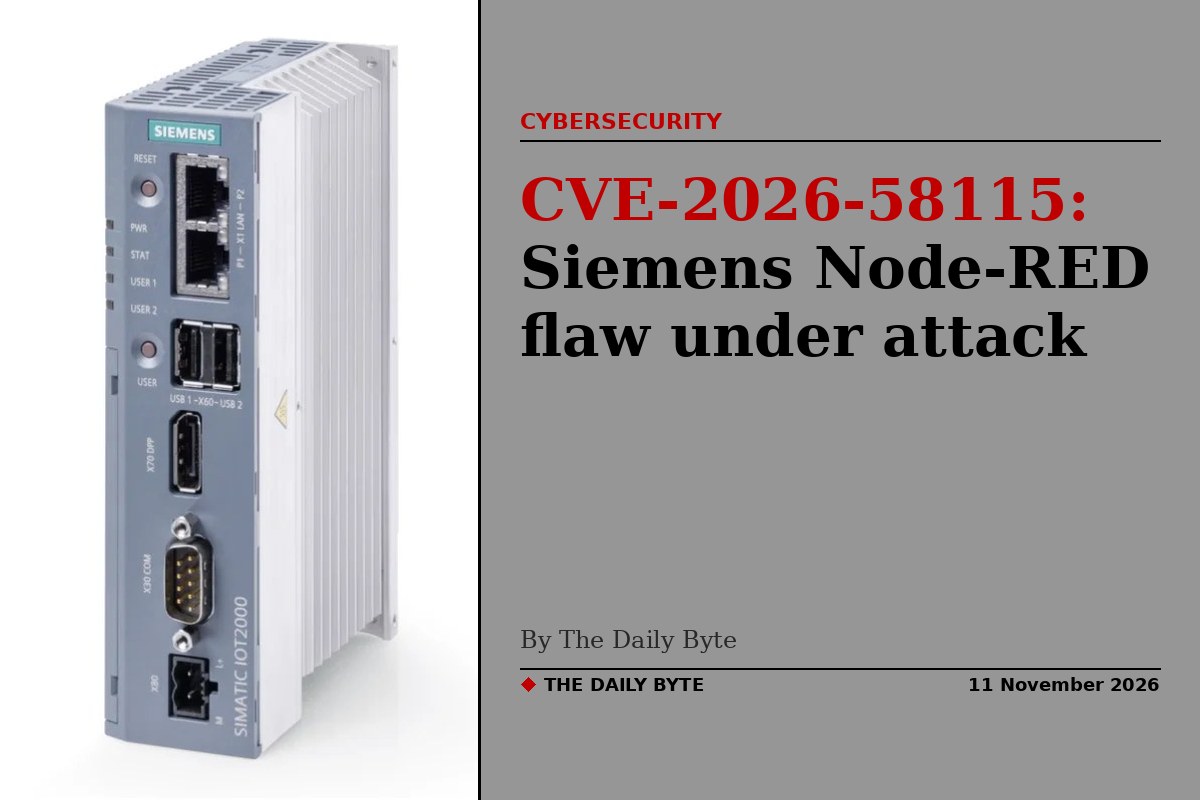
Attackers are actively exploiting a maximum-severity flaw in the Node-RED interface shipped with Siemens SIMATIC IoT2050 Advanced industrial gateways, security researchers have warned. Tracked as CVE-2026-58115, the flaw carries the highest possible CVSS score of 10.0, and a fix has been available since August — but any device that has not been updated is still exposed.
The flaw is a missing-authentication weakness in the Node-RED HTTP interface on the gateway. Node-RED is a flow-based programming tool used widely in factories, utilities and other industrial settings to wire together devices and automate processes. On affected SIMATIC IoT2050 Advanced units, the interface does not ask for a login at all, so anyone who can reach it over the network can deploy a flow and run commands on the device.
A flaw that needs no password
CVE-2026-58115 is classified as CWE-306, missing authentication for a critical function. It affects SIMATIC IoT2050 Advanced devices, order number 6ES7647-0BA00-1YA2, running Siemens Industrial OS with Node-RED installed, in all versions before V4.3.4.1.
The weakness is simple to exploit because of how Node-RED works. Two built-in node types do the attacker's job for them: an inject node fires a message on a schedule or at startup, and an exec node runs a shell command. Wire one to the other and the flow runs a command as soon as it is deployed, with no further interaction needed. An unauthenticated attacker can therefore gain full control of the gateway with a single web request.
Siemens published its advisory, SSA-834709, on 11 August 2026, and the US cyber agency CISA republished the warning as advisory ICSA-26-237-03 on 25 August. CISA lists the affected sectors as chemical, critical manufacturing, energy and transportation. Siemens' fix is to update to Industrial OS version V4.3.4.1 or later.
What attackers are doing with it
Vulnerability intelligence firm VulnCheck caught the first in-the-wild exploitation on 30 October 2026, when one of its decoy systems, known as a canary, recorded a complete attack. The request came from the IP address 4.201.105.116, which sits in Microsoft's network range and geolocates to Brazil. By 1 November, the same address had made 16 attempts against the flaw.
The attack deployed a Node-RED flow that downloaded and ran a Linux bot, fetching the binary from a server at 85.215.73.250 on port 8080 and saving it to a memory-backed location so nothing was written to disk. Later attempts from the same source delivered a staged shell script instead, and a second payload server at 45.194.90.57. Some attacks skipped the downloader entirely and planted persistent webshells, exposing a web endpoint that lets the attacker run commands later through a query parameter.
Researchers describe the activity as opportunistic mass scanning rather than a targeted attack on a particular plant. The same source address logged 125 hits against eight different vulnerabilities across VulnCheck's canary network in recent days, including older flaws in Apache Solr, Gitea, MLflow, Traefik and Joomla. VulnCheck has added CVE-2026-58115 to its own exploited-vulnerabilities catalogue, although it had not appeared in CISA's Known Exploited Vulnerabilities catalogue at the time of writing.
One important detail is that VulnCheck's canaries have not observed exploitation of this flaw in Siemens products specifically; the attacks it recorded targeted Node-RED instances in general. The risk to Siemens gateways is nevertheless direct, because the CVE is assigned to the Siemens device and the same unauthenticated interface is present on unpatched units.
What operators should do now
The first step is to update affected SIMATIC IoT2050 Advanced devices to Industrial OS V4.3.4.1 or later. Operators should also switch on Node-RED's built-in authentication, known as adminAuth, and take the interface off the public internet. Any Node-RED instance reachable from outside the network, Siemens or otherwise, is a target while this flaw is being scanned for.
Operators should also review the flows already deployed on their devices for anything unexpected, particularly exec nodes or HTTP endpoints they did not create, since some attackers are leaving webshells rather than bots. A webshell survives a reboot even if a memory-resident implant does not.
The case is a reminder that a patch published in August is only useful once it is installed. Three months after Siemens released the fix, attackers are still finding exposed devices and using a single request to take them over.


