CVE-2026-95377: Zenitel intercom flaw allows root access
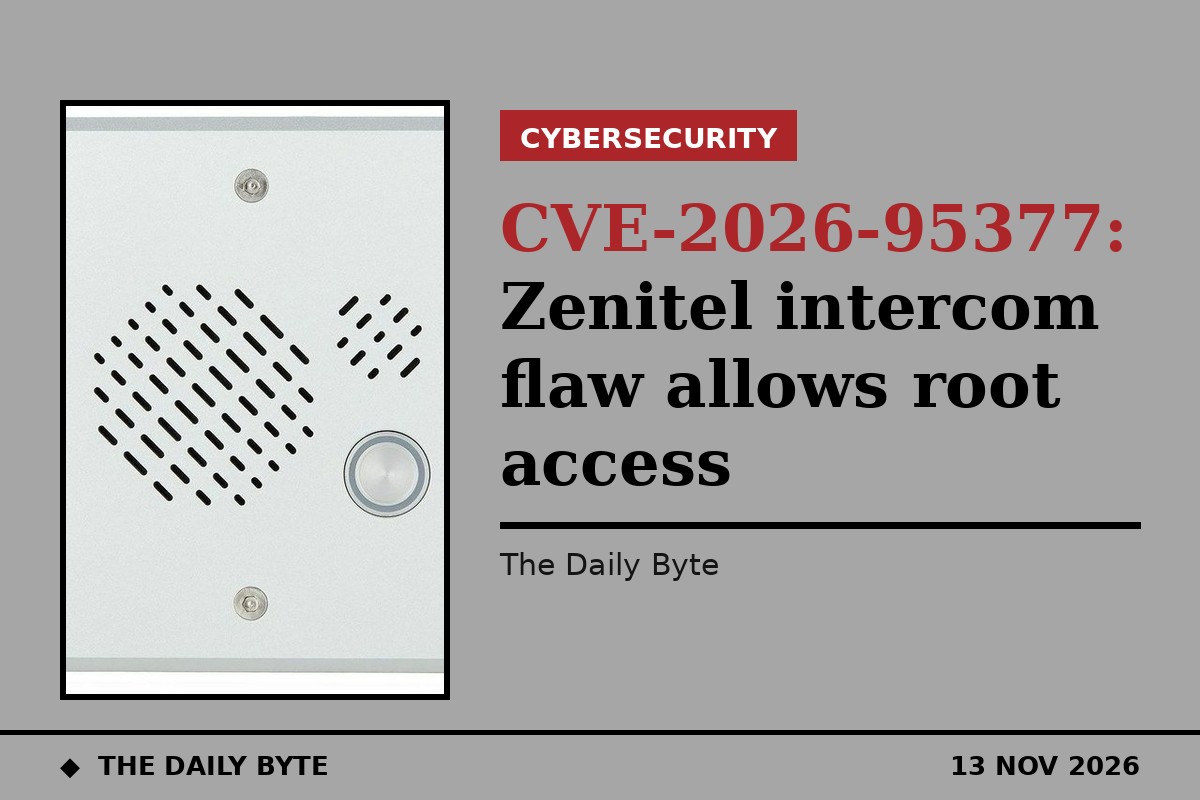
A critical vulnerability in Zenitel intercom devices lets an attacker on the local network run arbitrary commands as root, by sending a crafted value through the device's network provisioning process. The flaw, tracked as CVE-2026-95377, was published on 13 November 2026 and carries a critical CVSS 4.0 rating.
The problem sits in the TFTP provisioning module of Zenitel EdgeAudioClient, the software used by the company's audio and intercom stations. An unauthenticated attacker on the same network segment can use a rogue DHCP server to supply a crafted DHCP option 66 value, known as the TFTP Server Name, which the device passes to a shell without sanitisation.
Every boot is affected
Devices using DHCP, which is the default configuration, are affected on every boot and every lease renewal, because the device requests its provisioning settings each time. The affected devices are the VSFF6, VSFF8, VSFF8MP, VSFF8MN and VSFT models running EdgeAudioClient before version 9.6.3.0, or 10.x before version 10.1.3.0.
The same injection is also reachable through the config_update_tftp_server and sw_update_tftp_server configuration fields, by an attacker able to modify the device configuration. In both cases the result is the same: code execution with root privileges on a device that is often installed in public areas, transport hubs and industrial sites.
What to do
Because the attack needs only local-network access, the advisory is most urgent for sites where visitors or contractors can join the same network segment as the intercoms. Isolating voice and intercom devices on their own network segment, with only trusted DHCP servers allowed, removes the attacker's easiest path even before the patch is installed.
Zenitel has released fixed versions, and affected devices should be updated to EdgeAudioClient 9.6.3.0 or 10.1.3.0, or later, as applicable. Until the update is applied, organisations should restrict which DHCP servers their intercom devices can reach, segment the devices onto a trusted network, and check for unexpected configuration changes.
EdgeAudioClient runs on Zenitel intercom and audio stations installed in buildings, transport and industrial sites, where a compromised unit can be a foothold into a trusted internal network. The vendor advisory, reference A100K12404, covers both the 9.x and 10.x lines, so sites should check which line each device runs before applying the matching fix.
The flaw is classified as CWE-78, improper neutralisation of special elements used in an OS command. No exploitation in the wild has been reported in the advisory, but the combination of a default configuration, no authentication and root access makes this a patch-first issue for any site running the affected models. Sources: CVEFeed and Zenitel Security Advisory.


