Elecbrakes Trailer Brake Flaw Lets Attackers Brake Remotely
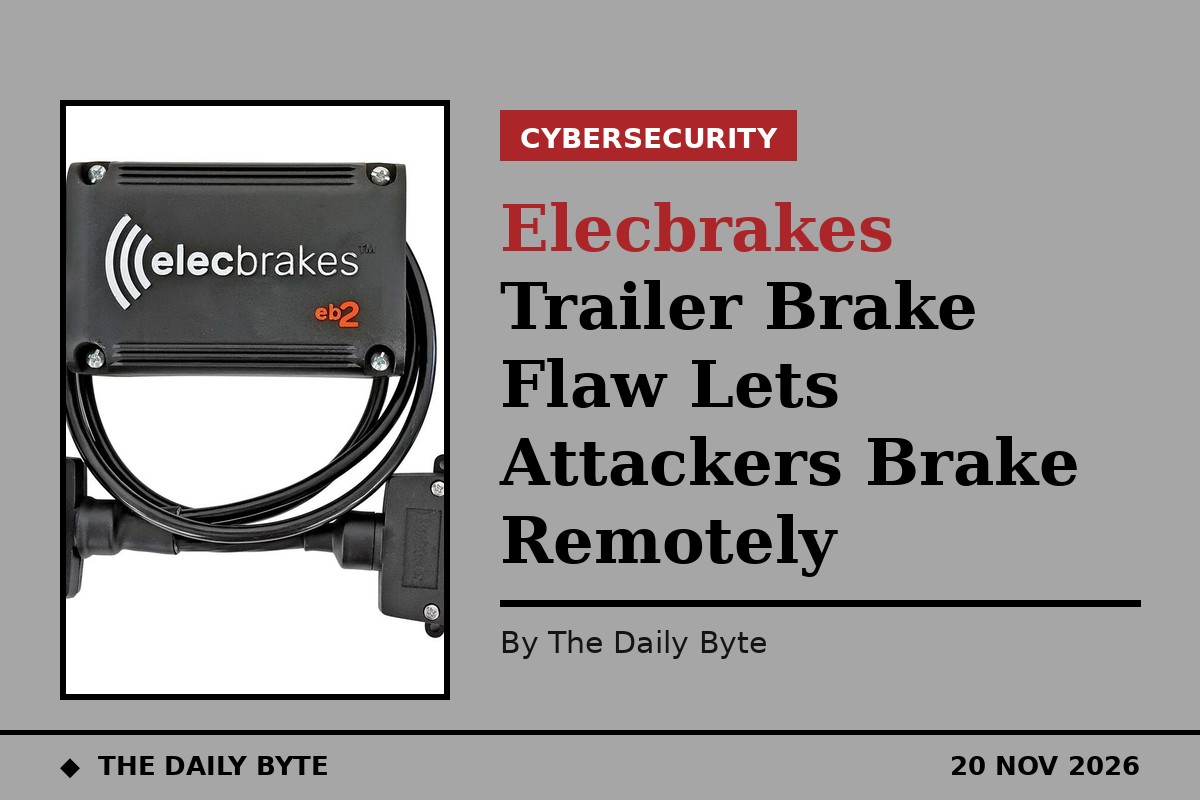
The United States cybersecurity agency has warned that a trailer brake controller sold in Australia and New Zealand can be operated by anyone nearby over Bluetooth, with no pairing, password or login required.
The Cybersecurity and Infrastructure Security Agency (CISA) published the warning on 19 November in advisory ICSA-26-323-02, covering three flaws in Elecbrakes EB2, VM1 and ELBC2000 brake controllers. CISA said successful exploitation “could allow an attacker to gain control of the brakes of a trailer, modify the firmware, disable the brake lights, modify the brake conditions or disable other critical safety features.”
Two of the three flaws are rated critical, each scoring 9.6 out of 10. The third, affecting the firmware update channel, is rated medium at 6.1. Because the controllers manage braking on trailers travelling on public roads, the flaws carry a direct road-safety risk rather than only a data risk.
The three flaws
The most serious flaw, tracked as CVE-2026-96805, is an unauthenticated command injection reachable over Bluetooth Low Energy. CISA said an in-range Bluetooth device could write to the control interface and influence braking “with no authentication or pairing”.
The second critical flaw, CVE-2026-125273, is the absence of replay or command-integrity protection. Commands carry no sequence numbers, nonces or session tokens, so a command captured once can be replayed later, and the last command persists across sessions.
The third flaw, CVE-2026-124281, is an unprotected firmware-update channel that may allow unauthorised firmware modification.
The flaws were reported to CISA by Patrick Forck and Jeremy McCarthy of Element Digital. Reporting on their research says a nearby device, roughly 10 to 100 metres away, could send a short command that applied the trailer’s brakes, and that the brakes released within two to five seconds once the Bluetooth connection dropped.
Which controllers are affected
CISA lists EB2 units running firmware 3.0.4.2.0 and earlier, VM1 units running versions before 1.3.4.2.1, and all ELBC2000 units as affected. The products are deployed in Australia and New Zealand, in the transportation systems sector, and the company is headquartered in Australia.
Fixed firmware is available for two of the three models. Elecbrakes has released EB2 version 3.0.4.4.3 and VM1 version 1.3.4.2.1, and CISA directs owners to open the Elecbrakes app and install the update. The researchers said they notified Elecbrakes in May and that fixed firmware arrived in July.
There is no fix yet for the ELBC2000, the predecessor to the EB2 and VM1, which is no longer sold. CISA says the vendor is determining how to address the vulnerabilities for that controller, and owners of the older model should contact Elecbrakes about their options.
What owners should do
Owners of EB2 and VM1 controllers should update through the Elecbrakes app now rather than waiting for a service visit. The update moves brake control behind an encrypted, bonded Bluetooth connection, according to the researchers. Owners should also note that older V2 remotes stop working after the update; Elecbrakes is exchanging them for a new V3 remote free of charge.
CISA also issued two further industrial control advisories on the same day, covering a flaw in OpenPLC Runtime that could allow unauthenticated admin accounts to be created, and an integer underflow in the libumqtt library. Neither of those advisories reports known exploitation either.
CISA said no known public exploitation specifically targeting the Elecbrakes vulnerabilities had been reported to it at the time of publication. That makes this a disclosure to act on before attacks appear, not evidence that any trailer has been tampered with on the road.
Sources
CISA advisory ICSA-26-323-02: Elecbrakes EB2, VM1, ELBC2000
Digital Advisors: Elecbrakes Bluetooth flaw: update your trailer brakes


