FreeSWITCH phone flaw exploited, patch urged now
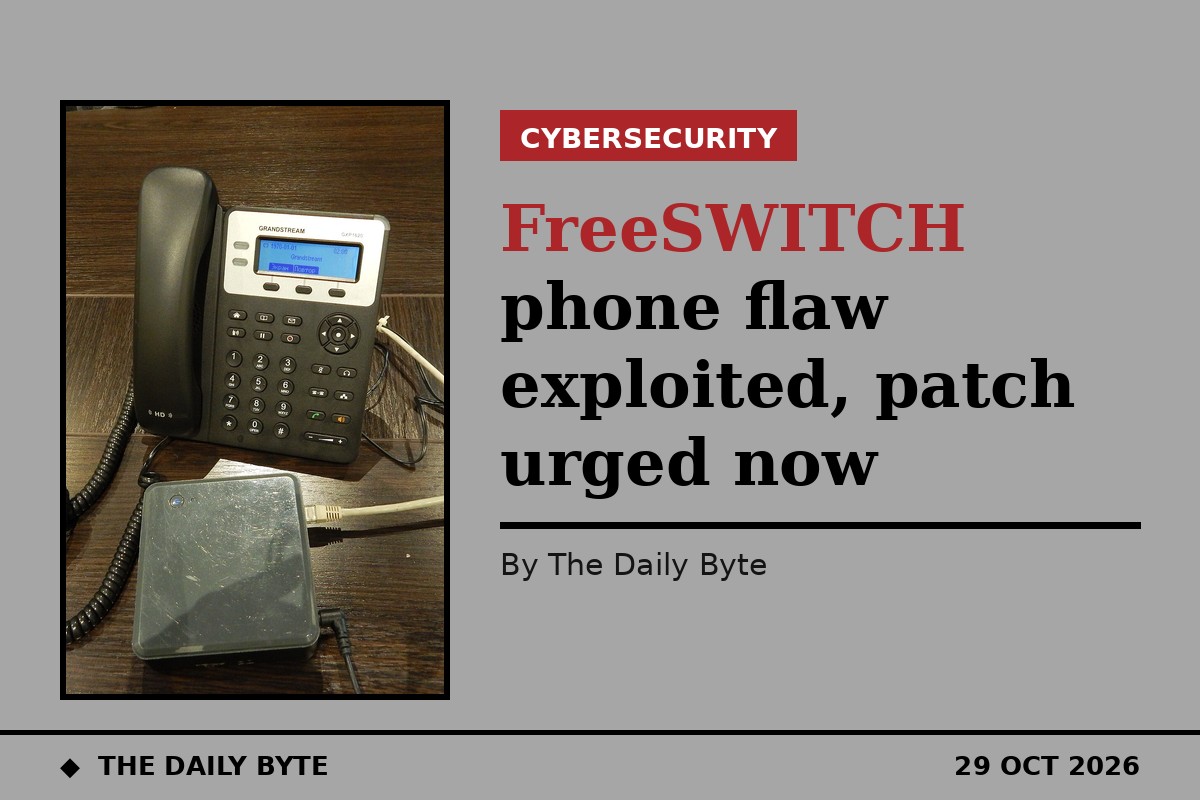
SignalWire has disclosed three critical vulnerabilities in FreeSWITCH, open-source telecom software powering business phone systems, WebRTC gateways and carrier switches. The most serious, CVE-2026-116779, is rated 9.8 out of 10 and allows remote code execution through inbound SIP messages — and, unlike the other two, it is being exploited in the wild.
Two more flaws in the same disclosure
The flaw is in how FreeSWITCH handles SIP chat messages. In default configurations where SIP chat is active, the software splits the recipient address of an incoming SIP MESSAGE on the "+" character and treats the first part as a chat protocol selector. Because one registered chat interface passes its argument directly to the command executor, an attacker can run arbitrary system commands. Servers keeping the default passwordless user account can be hit without any credentials at all.
Which versions are affected
The other two flaws are rated 9.1 each. CVE-2026-116785, in the XML-RPC module, is a heap overflow in WebSocket frame parsing triggerable before HTTP authentication. CVE-2026-116790 is a media-hijacking flaw: incoming ICE checks are processed without verifying their message-integrity attribute, so an unauthenticated attacker could redirect call media, causing dropped calls or eavesdropping. No active exploitation is claimed for these two flaws, and no public proof-of-concept exploit has been confirmed for any of the three.
Upgrade — and finish the configuration steps
Together, the three flaws affect all 1.10 and 1.11 releases before the patched builds. The WebSocket and ICE flaws are fixed in 1.11.2, while the exploited SIP flaw is fixed in 1.11.3, which disables the api chat protocol by default. Administrators should upgrade to FreeSWITCH 1.11.3, and the ice_verify_message_integrity variable must then be enabled manually. Unpatched servers should disable SIP chat and restrict RTP and HTTP ports at the firewall.
Sources: Meterpreter (SignalWire advisories), Enable Security (earlier api-chat abuse report).