iRhythm data breach affects 8.2 million patients
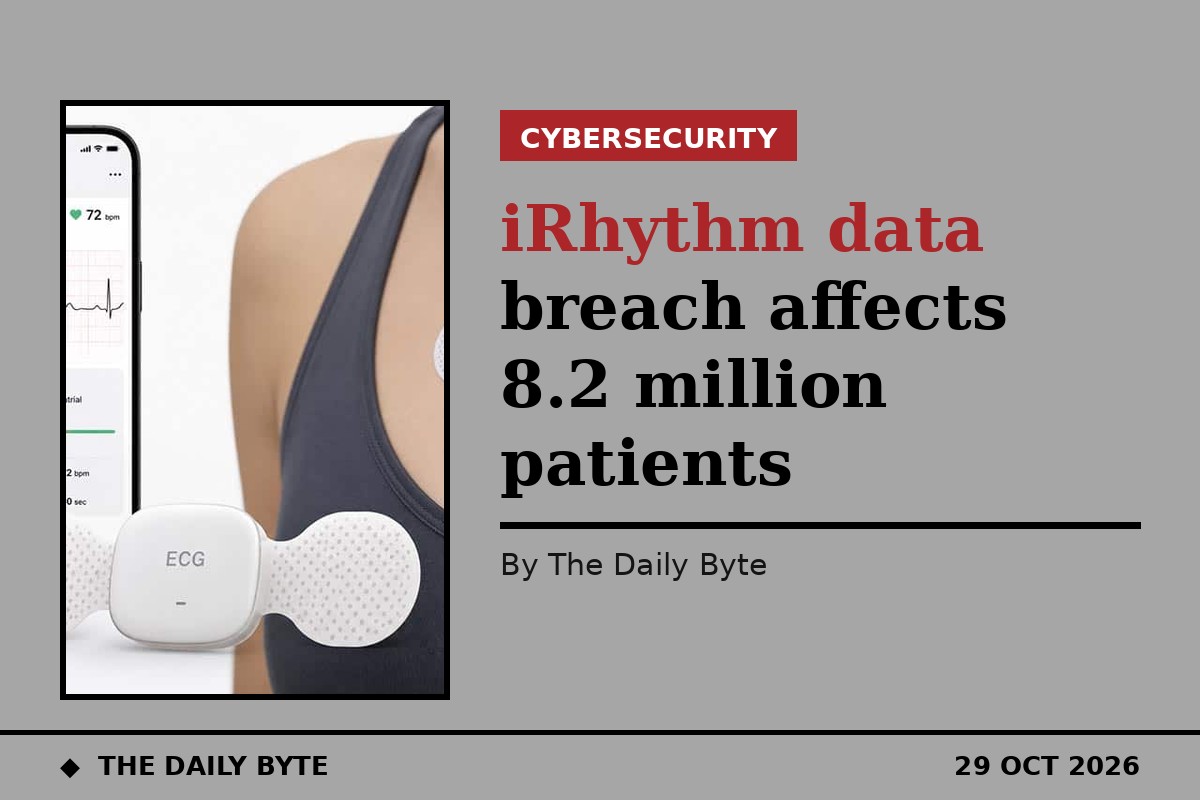
A data breach at iRhythm Technologies, the company behind the Zio wearable heart monitor, now stands at 8,179,772 affected individuals according to a regulatory filing reported on 29 October 2026. The figure, first disclosed in a filing with the Oregon Attorney General, is the largest confirmed scope yet for an incident the company first disclosed in June 2026. Because iRhythm says it serves more than 8 million patients in the United States and Europe, the filing suggests the breach could potentially touch almost its entire patient base, although the company itself has not published its own national total.
Heart-monitor breach toll reaches 8.2 million
iRhythm detected unauthorised access on 8 June 2026, and the following day a threat actor contacted the company claiming to have stolen data and demanding payment in exchange for not releasing it. According to the company's filings, the attacker reached certain third-party-hosted business applications through social engineering, rather than breaking into its clinical systems or the Zio devices themselves. The company says its products, medical device systems, manufacturing and patient safety were not affected, and it has not disclosed whether any extortion payment was made. Notification letters to affected individuals began in early October, nearly four months after detection.
What happened in June
The exposed information includes patient names, addresses, dates of birth, email addresses and phone numbers, along with account numbers, device serial numbers, insurance numbers and dates of service. iRhythm says it does not retain financial account or payment card data, and that it has no evidence the information has been or will be used to commit identity theft. The incident is a reminder that third-party business applications can be the weakest link in healthcare security, even when the medical devices themselves remain untouched.
What data was exposed
Sources: SecurityWeek via Cybernoz, BankInfoSecurity.