Linksys E8450 flaw scores 10.0 with no fix available
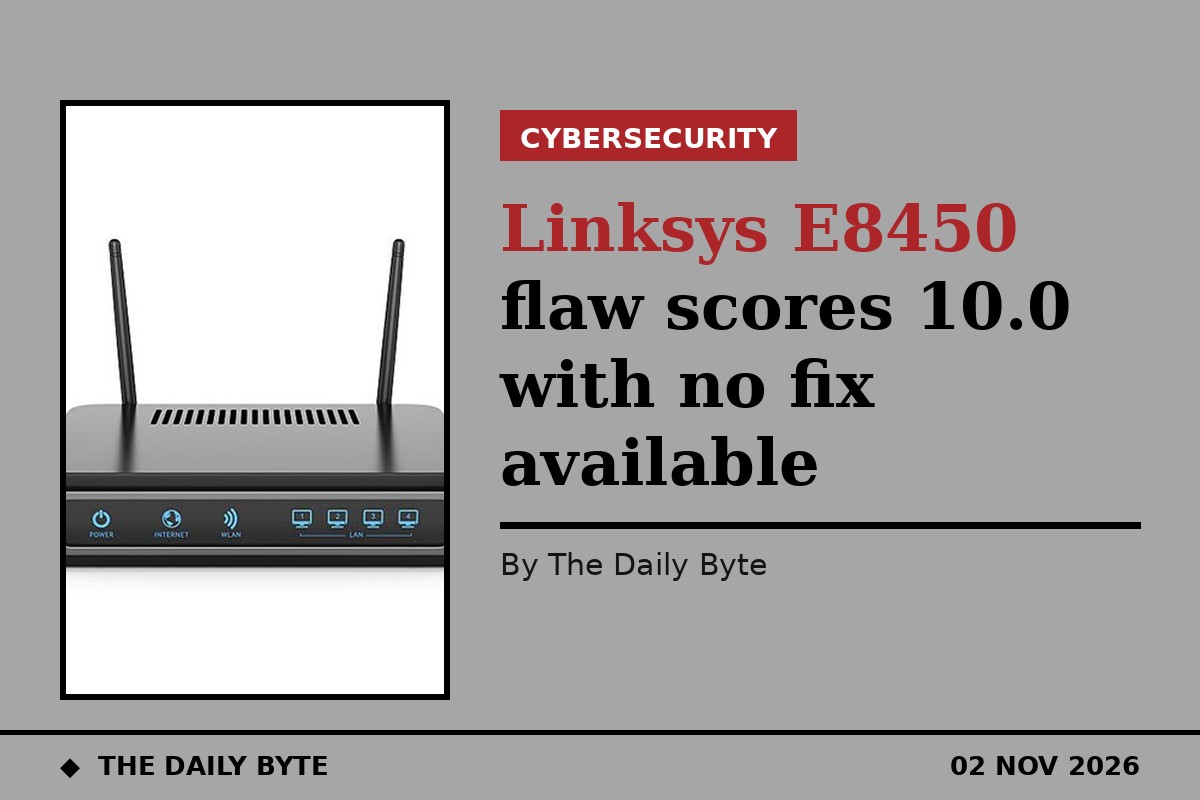
A critical flaw in the Linksys E8450 router has been given the maximum severity score of 10.0, with no fix listed in the vulnerability record. The flaw, tracked as CVE-2026-120283, affects firmware version 1.2.00.360516 and was published in the US National Vulnerability Database on 2 November 2026.
The problem sits in the router's web management interface, in a file called portal.cgi. According to the CVE record summarised by StackFlag, manipulation of a field called hidden_timezone can trigger a stack-based buffer overflow. In plain terms, the router sets aside a limited amount of space for a piece of information, and an attacker sends more than fits, spilling over into areas that should not be overwritten.
Remote attack, no vendor response recorded
The CVE record states that the attack can be executed remotely. Rainier IT, reporting on the National Vulnerability Database entry, notes that the record does not make clear whether an attacker must already be on the local network or can reach the router from the internet, so owners should plan for both possibilities. No attacks using the flaw were known from the database entry.
Significantly, the record states that the vendor was contacted early about the disclosure but did not respond in any way. That leaves owners without a published patch at the time of writing, and the record lists no fixed version.
What owners should do now
Until a fix appears, steps reported by Rainier IT include switching off remote management so the settings page is not reachable from the internet, changing the admin password to a long and unique one, and checking Linksys support pages regularly for a firmware update.
Sources: National Vulnerability Database via Rainier IT; StackFlag CVE record summary.