Synology NAS owners warned as C3RB3R ransomware spreads
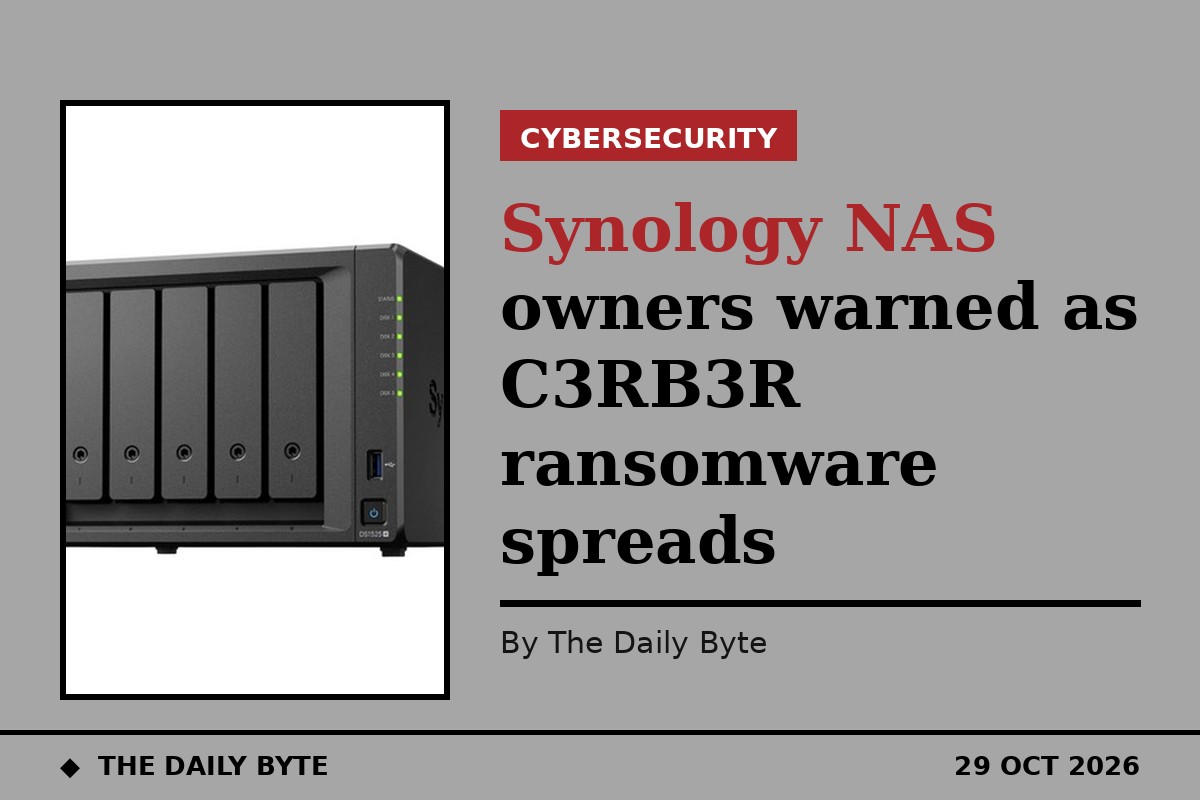
Owners of Synology network-attached storage devices are facing a fresh ransomware wave that encrypts personal files and demands payment in bitcoin. Reports collected since early October link the attacks to C3RB3R, a variant of the long-running Cerber ransomware family that has targeted storage devices for years. Affected files gain the extension .L0CK3D, while a ransom note named read-me3.txt is left in each encrypted folder, directing victims to a site on the Tor network.
Patched flaws at the centre of the wave
Security analysts assessing the wave point to two flaws in Synology's DiskStation Manager software, CVE-2026-13639 and CVE-2026-13684, which Synology fixed on 18 September 2026 in advisory Synology-SA-26:13. Devices left exposed directly to the internet, through port forwarding or remote-access features, are the most exposed. One incident-response team reports a victim already running the latest DSM 7.4.1 release, with the entry point still being traced, which suggests a new flaw, a third-party package or leaked credentials cannot yet be ruled out.
How owners can protect their data
Owners should update DSM to a fixed release, remove port forwards, switch off QuickConnect and other direct external access, and use a virtual private network for remote access instead. Unused packages, containers and accounts should be removed, two-factor authentication switched on, and shared-folder snapshots enabled with tamper protection, alongside one offline backup kept disconnected from the network. If files are already encrypted, recovery specialists advise keeping the device powered on but cutting it off from the internet, preserving the ransom note and logs, and checking surviving snapshots. There is no public decryptor for this variant, and paying is discouraged.
Sources: NoRansom, SecurityOnline.