TOTOLINK Router Hit By Seven Critical Flaws In A Day
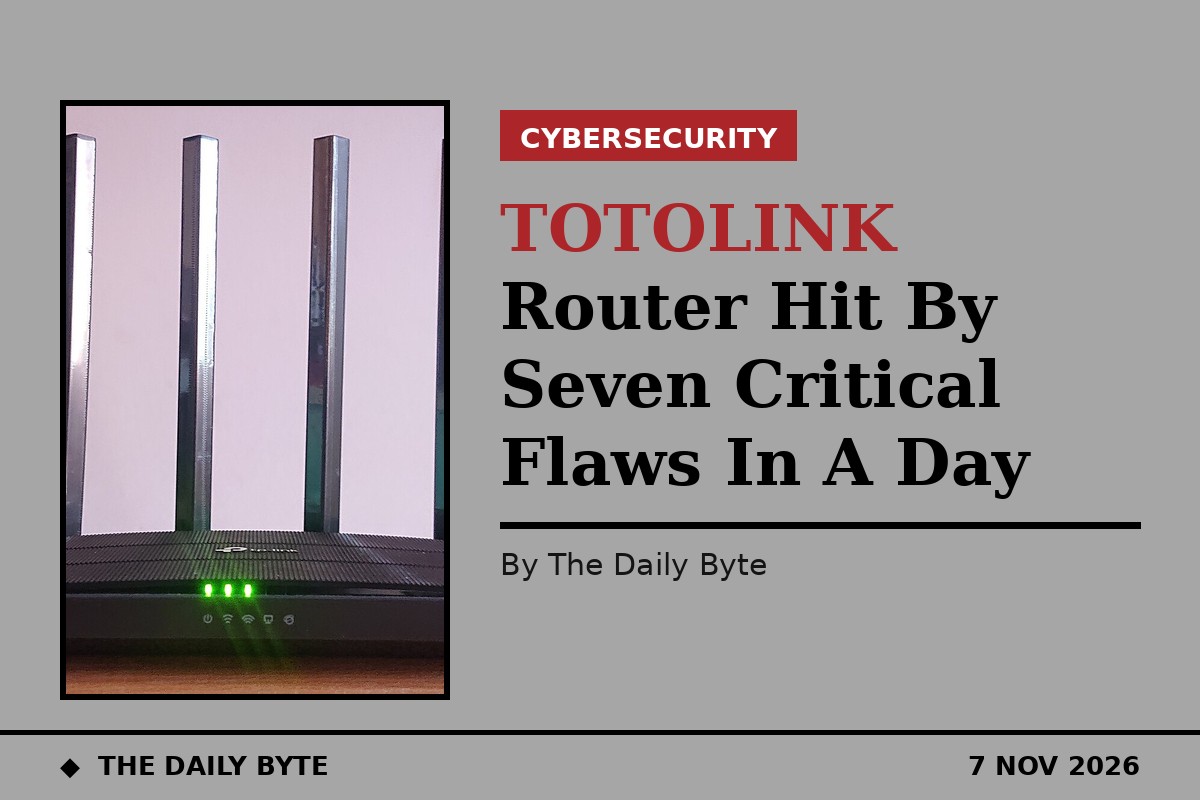
Seven critical vulnerabilities were disclosed in a single day in TOTOLINK's CA300-PoE router, all of them buffer overflows in the same firmware version, all remotely exploitable, and all with public exploit code already available.
The flaws affect firmware version 6.2c.884 of the CA300-PoE, a device used to extend wireless coverage. They were all published on 7 November 2026. The most severe, CVE-2026-123957, scores 9.4 and sits in the setIpQosRules function of the router's web interface, where manipulating the ipStart argument can overflow the device's memory.
The other flaws follow the same pattern in different functions of the same interface file: CVE-2026-123958 in setLanConfig, CVE-2026-123959 in setLanguageCfg, CVE-2026-123960 in setWanConfig, CVE-2026-123961 in setWiFiBasicConfig, CVE-2026-124057 in setWiFiMultipleConfig, and CVE-2026-124058 in setWiFiRepeaterConfig. Each one can be triggered remotely, and each carries a critical score of 9.1 or 9.4.
A buffer overflow of this kind can crash the device or, in the worst case, allow an attacker to execute code on it. Because the flaws are in the router's web interface, any device with that interface reachable over a network is exposed.
No fixed firmware version is listed in the CVE records, so owners cannot patch the problem yet. Until a fix appears, the safest steps are to keep the router's administration pages off the internet, restrict access to trusted devices only, and check TOTOLINK's website for an update.
The cluster is a reminder that a single firmware release can carry many flaws at once, and that routers and access points need the same patching discipline as any other device on the network.
[Source: radar.offseq.com](https://radar.offseq.com/threat/a-vulnerability-was-determined-in-totolink-ca300-poe-62c884-cve-2026-123957-6b846c9df7d9739f) | [Source: opencve.mandarin-it.de](https://opencve.mandarin-it.de/cve/CVE-2026-123957)