WhiteArmor claims Clínica La Sagrada Familia breach
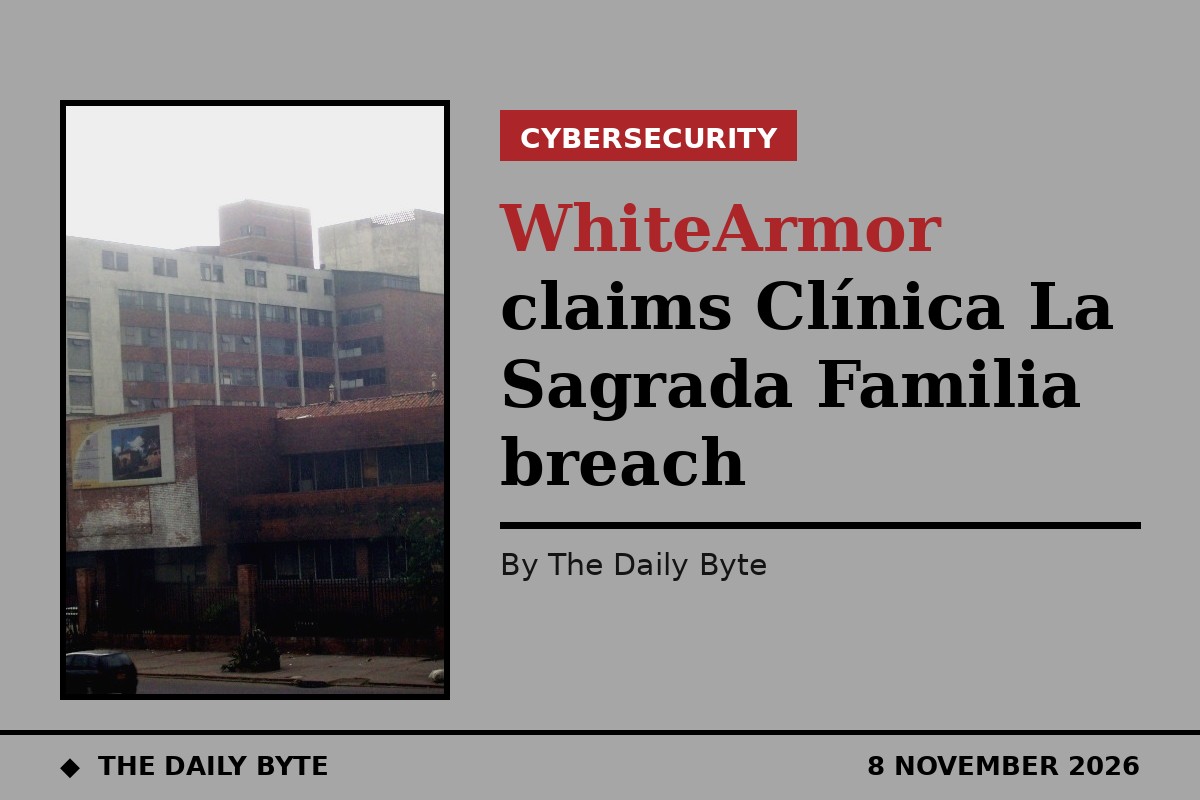
The ransomware group WhiteArmor claims it has stolen the records of more than 250,000 patients from a private hospital in Colombia and is demanding a $2 million ransom in Bitcoin, according to threat intelligence reports published on 8 November. The claim has not been independently confirmed, and no statement from the hospital has been reported.
The claim concerns Clínica La Sagrada Familia S.A.S., a private healthcare provider in Colombia’s Eje Cafetero coffee-growing region. The clinic offers medium- and high-complexity medical services, online appointment booking and advanced imaging, including a 160-slice CT scanner, according to the reporting.
The attackers’ message, quoted in the threat intelligence report, says the group holds 254,670 patient identities linked to Colombian government ID numbers, along with about 598.7 million rows of clinical, financial and identity data spread across 4,573 tables taken from the hospital’s production database. The message also lists 691,000 admissions, 34.5 million medical-history rows and 1.5 million invoices, as well as complete pharmacy and laboratory records and staff login credentials protected only by MD5 hashing, an older method that is straightforward to crack. The group demands $2,000,000 in Bitcoin.
None of those figures has been verified by an independent source. The incident was logged in the early hours of 8 November, with the breach dated 02:45 UTC and the discovery logged at 03:33 UTC. Threat monitoring cited in a second report notes that no confirmed evidence of data theft, exposed patient records or disruption to clinical services was included in the material available so far. A listing on a ransomware leak site is a claim by the attackers, not proof that a breach took place or that the data described was actually taken.
Healthcare providers are a frequent ransomware target because patient records combine identity documents, medical histories and payment details in one place. Many groups now use double extortion: they encrypt systems and threaten to publish stolen data unless a ransom is paid, which puts pressure on hospitals even when backups would allow them to restore their own systems. If the claimed data is genuine, the patients affected would face a heightened risk of identity fraud and of phishing messages pretending to come from the clinic.
What happens next depends on verification. The clinic has not been reported as confirming or denying the incident, and neither the volume of data nor the ransom demand has been corroborated. Patients and staff should watch for an official statement from the clinic and be wary of unexpected messages asking for personal details or payments. Until independent evidence appears, the WhiteArmor claim should be treated as an allegation, not as an established breach. Read the original reporting on HookPhish.


