XaocMail phishing campaign drops Phantom53 Havoc
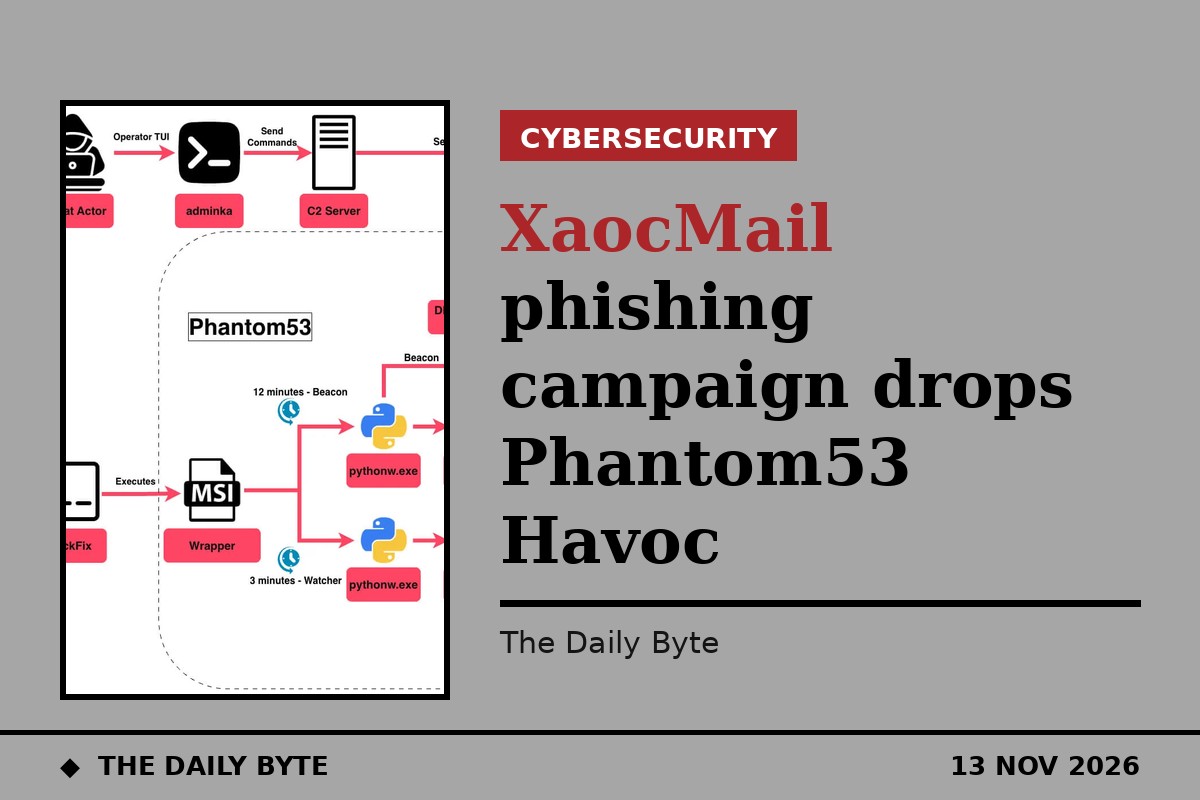
Security researchers have exposed an active phishing campaign run by a Russian-speaking group that chains three tools together to break into organisations across Latin America, Asia and Europe. SOCRadar disclosed the campaign, dubbed XaocMail, on 13 November 2026, warning that it uses AI-built infrastructure and is still running.
The attack starts with XaocMail, a self-hosted phishing platform that sends personalised emails disguised as document-sharing notifications from Google Docs, Adobe Acrobat or Office 365. Victims who click through reach a ClickFix page that tricks them into running a command, which downloads an installer for the second tool, Phantom53.
Hidden control channel
Phantom53 is a command-and-control framework that hides its traffic inside DNS-over-HTTPS queries to public resolvers such as Google and Cloudflare, which are rarely inspected. Its beacon checks in every 12 minutes, while a separate watcher can load the Havoc post-exploitation framework into memory on demand for high-value targets.
The operators built in resilience: a week-keyed domain-generation algorithm provides fallback command servers if the active domain is blocked, and the whole delivery chain runs on legitimate Cloudflare services. SOCRadar also found signs that the code was developed with AI help, including Claude Code task structures in the codebase.
Targets across three continents
Preparation began in October 2025, with phishing tests and framework development through early 2026 before the campaign launched in August 2026. Targets span technology, finance, education, government, logistics and manufacturing, with a slight tilt towards technology. Organisations should treat unexpected document-sharing emails with suspicion, never follow ClickFix-style copy-and-paste instructions, and watch for the campaign indicators SOCRadar has published.
Sources: SOCRadar and IT Security News.

