Zyxel June patch failed as GS1900 attacks used a new flaw
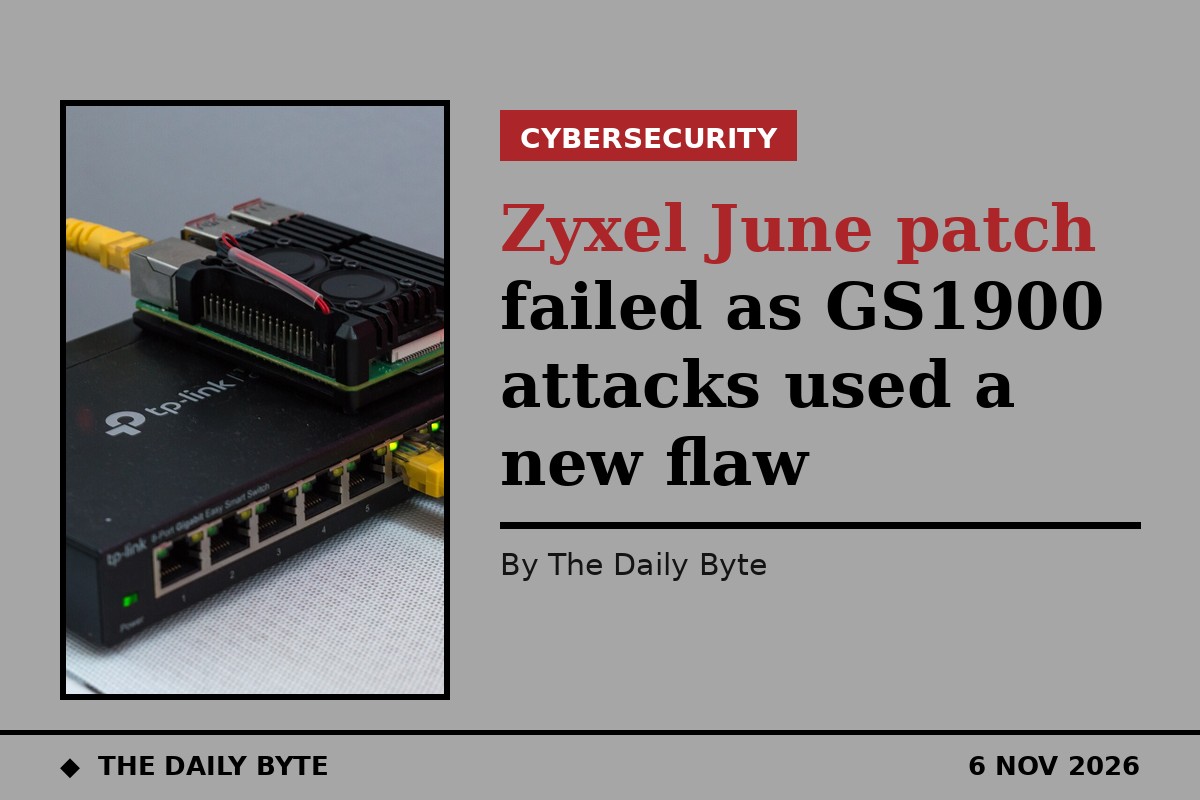
Follow-up: this post updates our 4 November report on the Zyxel GS1900 attacks. The wave of attacks on GS1900 switches was not stopped by the patch meant to fix it — because the attackers were exploiting a different vulnerability all along, Binarly reported on 3 November.
The patch that did not work
GreyNoise reported in September that attackers had compromised roughly 996 GS1900 switches in 48 countries from around 17 August, stealing switch configurations, hashed root credentials and network details, and blamed CVE-2026-7273, patched by Zyxel on 16 June. But when Binarly tested all ten firmware releases shipped as the June fix on 28 September, every one remained open to the exploit in the attacks. The June patch had added a parameter-count check — but it ran only after the unsafe copy had already happened, so it did not address the vulnerability.
What the new flaw is
Binarly notified Zyxel on 29 September; Zyxel confirmed the flaw on 11 October, shipped fixed firmware on 22 October and published its advisory on 3 November, assigning it CVE-2026-107441. It is an out-of-bounds write in the switches' CGI web-management program: an unauthenticated attacker can send crafted HTTP requests and run operating system commands. Zyxel rates it 8.8; Binarly rates it 9.8, needing only network access to the management service. Canada's Centre for Cyber Security noted on 4 November that open-source reporting says the flaw is exploited in the wild.
What owners must do
Ten GS1900 models on firmware 2.90 Patch 2 and earlier are affected; Patch 3 builds close the hole. Zyxel's advisory lists the June releases among the affected versions, so switches updated in June still need the new firmware. The 996-switch figure describes the campaign originally attributed to the earlier flaw, not a victim count for this CVE alone.
Sources: SecurityWeek, Zyxel switch hacks blamed on patched flaw actually exploited a zero-day, 5 November 2026; Infosecurity Magazine, Zyxel GS1900 patch missed flaw, 5 November 2026; eSecurityPlanet, Zyxel GS1900 zero-day CVE-2026-107441, 5 November 2026.