Ray-Ban Meta Glasses Hacked to Run Unapproved Code
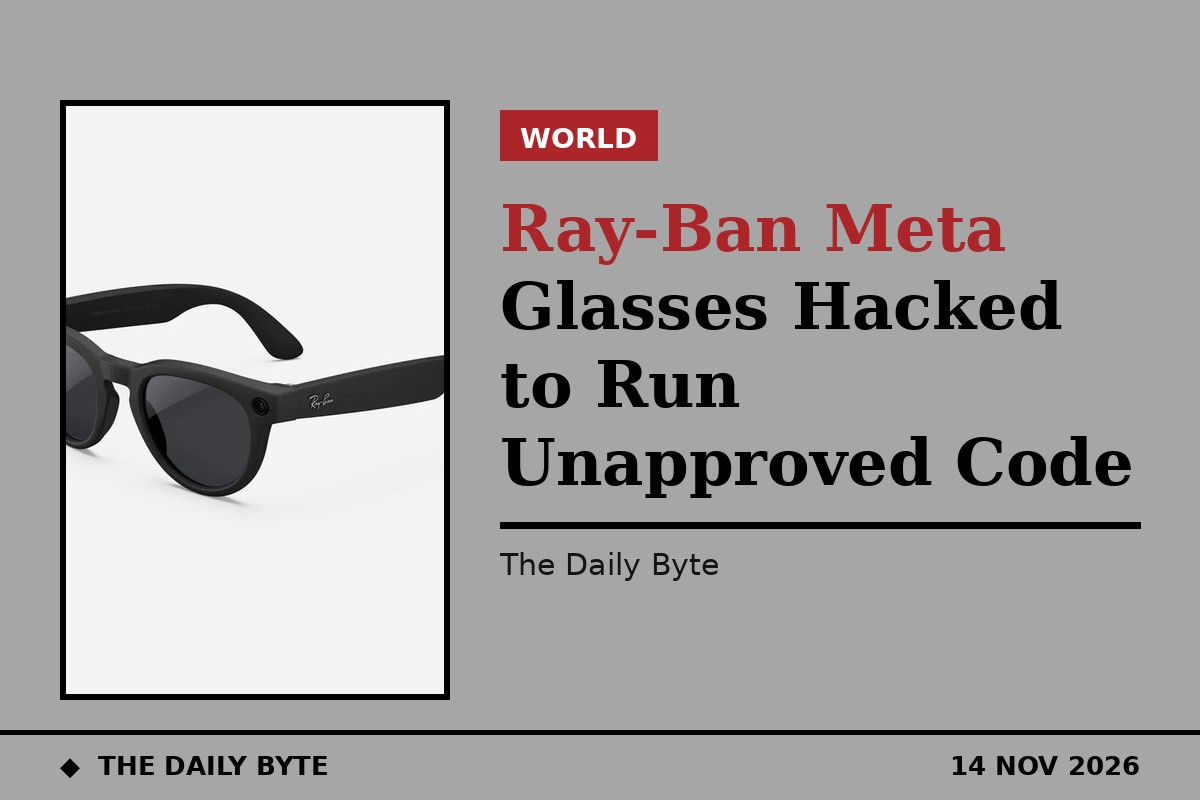
A security researcher has bypassed the software protections on Meta's Ray-Ban smart glasses and run her own code on the device, in findings that raise fresh questions about who controls a wearable that carries a camera, microphones and a wireless connection on its wearer's face all day.
Vulnerability researcher Paula Pamoutaf, known online as pamoutaf, published her findings on 6 November 2026 after months of work that began in July with a borrowed pair of the glasses. Rather than taking the hardware apart, she analysed the Meta AI companion app that pairs with the glasses and handles synchronisation and firmware updates, and intercepted data from an over-the-air update to obtain a complete firmware package.
Unsigned apps slipped past the checks
Her attention turned to Meta's Device Access Toolkit, the software that lets developers build apps working with the glasses' camera, audio and motion features. She found that firmware version 126 and earlier did not verify that the toolkit's Android application package was signed by Meta. By modifying data delivered through the paired smartphone, she substituted a self-signed application, launched Meta's Camera Access sample app to start a session, and established an interactive command shell over Wi-Fi Direct.
The shell let her run commands within the installed application's security context. The demonstration did not establish root access or unrestricted control of the glasses, and the researcher used audio beeps in place of log messages because the glasses have no screen.
Meta's patch was bypassed too
After about five days, the researcher lost shell access, and she could not determine whether her own actions or Meta had ended it. Firmware version 127 then began enforcing application signature verification, blocking the original installation method. But the protection depended on a setting in a configuration file that the phone fetches from Meta's servers and passes to the glasses. The glasses checked the file's structure but not whether its contents had been altered, so changing a single value disabled signature verification and let the self-signed application be installed again.
The researcher reported the findings through Meta's bug bounty programme and received approval to publish her account. She took that approval as a possible indication of a fix rather than confirmation. No verified patch date or final firmware version resolving the issue has been disclosed, and whether the method still works on updated glasses remains unconfirmed.
What it means for owners
It is important to be clear about the limits of the research. The published attack required deliberate manipulation of software on a paired smartphone. It did not demonstrate a method for remotely compromising another person's glasses without such access, and the researcher did not report stealing photographs, making covert recordings, or exploiting devices belonging to unsuspecting owners.
Even so, security researchers say the stakes are high for this category of device. Malwarebytes warned that malicious code could send stored recordings from the glasses to an attacker, and its researcher Pieter Arntz said a wearable that can be made to run unapproved code goes beyond a privacy question and becomes a security question about who controls the device.
Meta's Ray-Ban glasses were already under heavy scrutiny. Privacy advocates and consumer groups have raised concerns about covert filming, a major Dutch eyewear chain suspended sales of the glasses, and New York banned Meta and other smart glasses from more than 1,240 state courts. The findings also reopened a debate among technologists about whether owners should be allowed to run their own code on hardware they bought, a point many raised after the disclosure. Sources: Cybernews and TechTimes UK.