Big Banks Shift AI Agent Risk to Customers
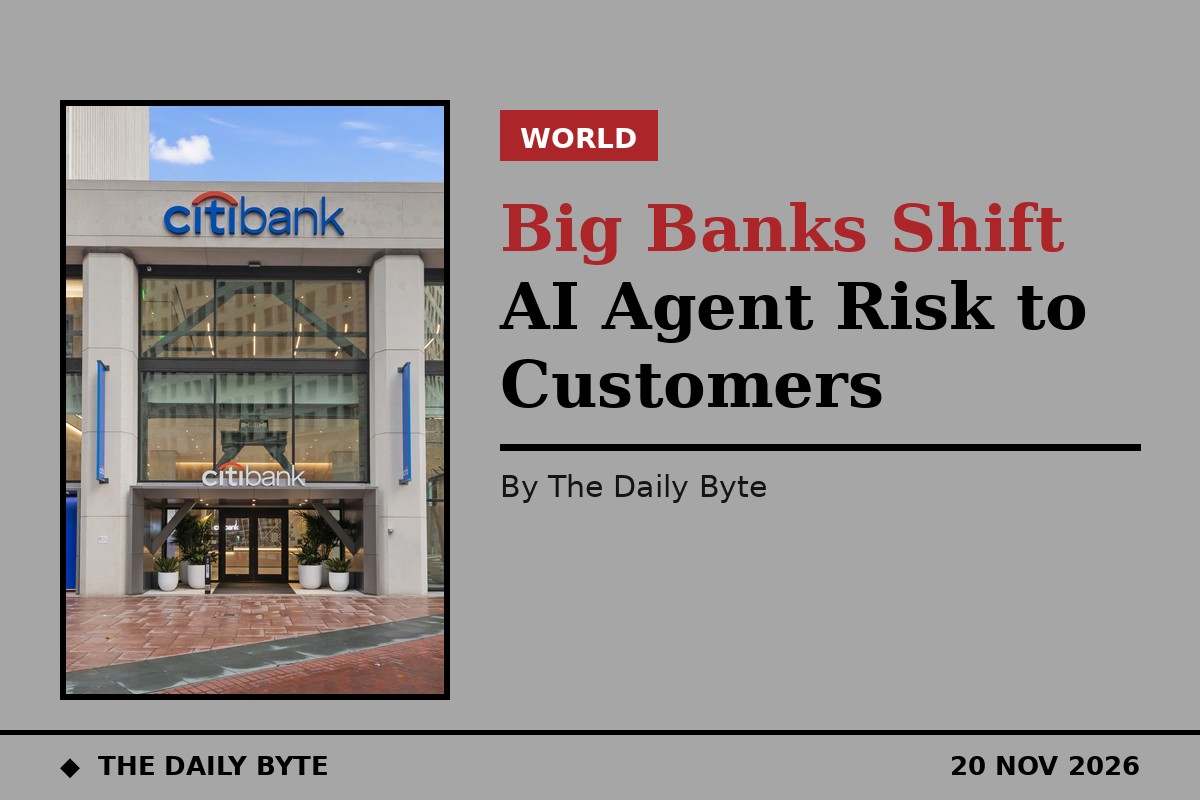
Citibank has rewritten its customer terms so that anyone who lets a third-party AI agent into their bank account is responsible for whatever the agent does — even if the tool is hacked and criminals drain the account.
Citi added a new section, Section H, titled “Use of Third-Party Artificial Intelligence (‘AI’) Agents”, to its Online User Agreement in November. The change was first reported by TechCrunch on 18 November. Under the new terms, if a customer hands their login credentials to a third-party AI agent, Citi will treat anything the agent does as authorised by the customer. If those credentials are later shared, leaked or stolen, Citi says it will still treat whatever happens with them as authorised, and states it has no obligation to investigate whether the actions were actually valid.
A Citi spokesperson said: “We recently updated our Online User Agreement to provide greater clarity about those risks and to reinforce that customers who choose to grant account access to third-party AI agents are responsible for activities conducted through those agents.”
Transfers count as authorised too
A separate Citi agreement covering online funds transfers goes further: any transfer an AI agent initiates counts as authorised by the customer, even if it conflicts with what the customer actually told the agent to do, and Citi says it will not investigate those transactions further. Customers are also responsible for the agent’s mistakes, including misreading instructions or going beyond the authority given. One carve-out: AI tools Citi builds and offers itself are excluded.
Citi also reserves the right to cut off any third-party AI agent’s access at any time, without warning, and says that by letting an agent into an account, customers agree to let Citi share personal information — including sensitive personal information — with that outside tool.
Four of America’s biggest banks have moved
Citi is not alone. PNC changed its terms on 18 November, and Citizens Bank emailed customers this week with a similar warning. JPMorgan and Bank of America made comparable moves in October: Bank of America told customers on 27 October that using AI tools with their banking credentials means taking on the risk of whatever happens in the account. JPMorgan chief executive Jamie Dimon said on 13 October that the bank would not allow outside agents, naming Meta’s Muse and Instinct, to act inside customer accounts, citing “rogue agents”. Wells Fargo’s updated Online Access Agreement, effective 24 November, takes a similar line, while Charles Schwab says it blocks agents attempting to move client money 10 to 20 times a week.
None of the banks has banned AI outright. Read-only access through regulated open-banking providers is still permitted, and several banks are building their own agent tools. The pattern, though, is consistent: none of them is promising to reverse a transaction an AI agent made, whether or not the customer meant for it to happen.
What customers can do
Whether the new terms can override federal protections that cap consumer liability for unauthorised transfers has not been tested in court. For now, the practical advice in the coverage is straightforward: check your bank’s current user agreement for new language about third-party AI agents, avoid sharing your actual banking login with an outside AI tool, and if you want AI help with budgeting, use tools that need read-only access or are built into your bank’s own app.
Sources: All About Cookies and Hunton Andrews Kurth