CVE-2026-0004: AMD Turin flaw risks data leaks in VMs
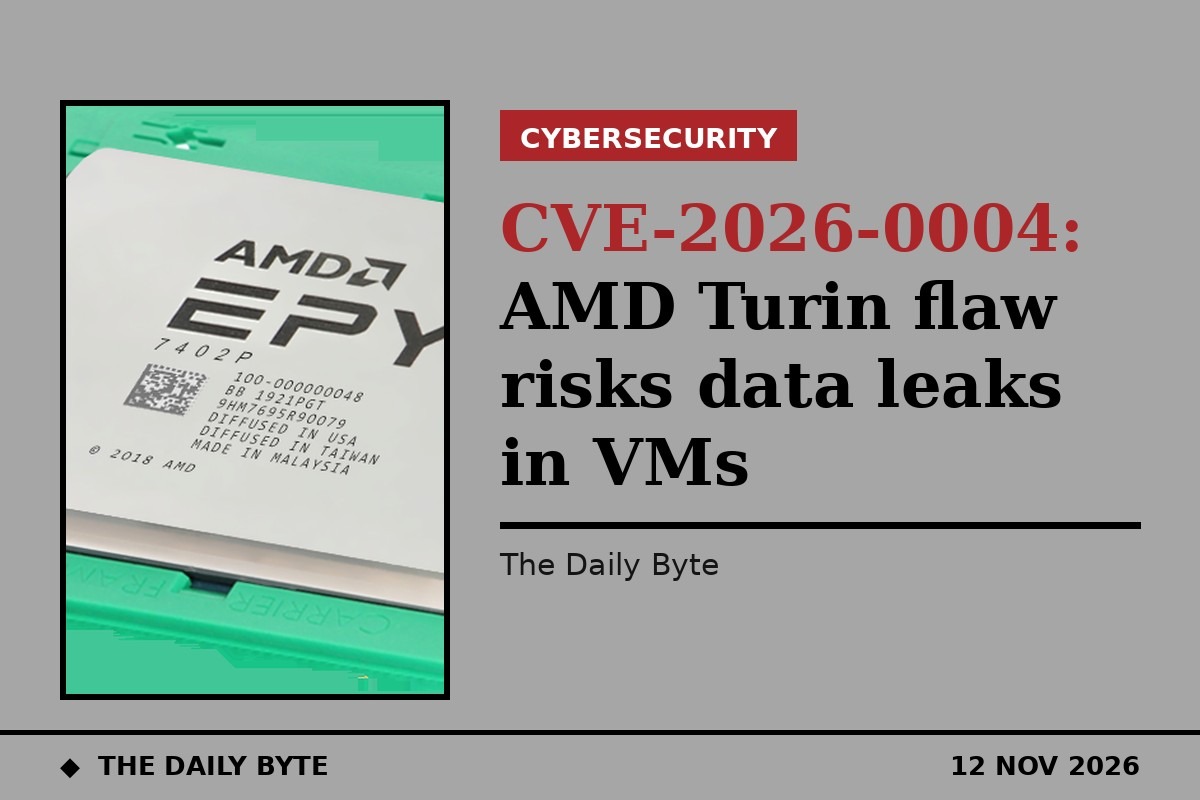
Google Cloud has warned customers running virtual machines on AMD's fifth-generation EPYC processors, codenamed Turin, that three processor flaws could let an attacker infer sensitive data from other processes or the operating-system kernel inside a virtual machine. The newest of the three, CVE-2026-0004, was disclosed this week.
All three flaws belong to a family known as Transient Scheduler Attacks, which exploit how the processor handles instructions during transient execution. Two of them, TSA-SQ (CVE-2024-36350) and TSA-L1 (CVE-2024-36357), were first disclosed on 8 July 2025 for earlier EPYC processors. AMD has now confirmed that its Zen 5 processors, including Turin, are affected differently from what was previously understood. The new flaw, CVE-2026-0004, which the Xen Project calls TSA-Fill, may let an attacker who can already run code on a system infer data held in the processor's Level 1 data cache.
Which Google Cloud machines are affected
The affected machine series are C4D, N4D, H4D, Z4D and G4, including bare-metal instances of C4D and Z4D. Google rates the issue as medium severity, while AMD describes all three flaws as local attacks with high attack complexity that require only low privileges. Neither Google nor AMD has reported evidence of active exploitation, and none of the three vulnerabilities is listed in the US CISA Known Exploited Vulnerabilities catalogue.
Patching needs a full stop and start
Customers must install the relevant guest operating-system updates and then perform a full stop-and-start of each affected virtual machine; simply rebooting the guest is not enough to switch on the protections. Google said it would update the CPU information reported by virtual machines this week so patched guest kernels can enable their mitigations. Debian has so far fixed CVE-2026-0004 in its Linux kernel only in its unstable branch.
Sources: The Hacker News, The 420