CVE-2026-126259: FortiOS flaw gives super-admin access
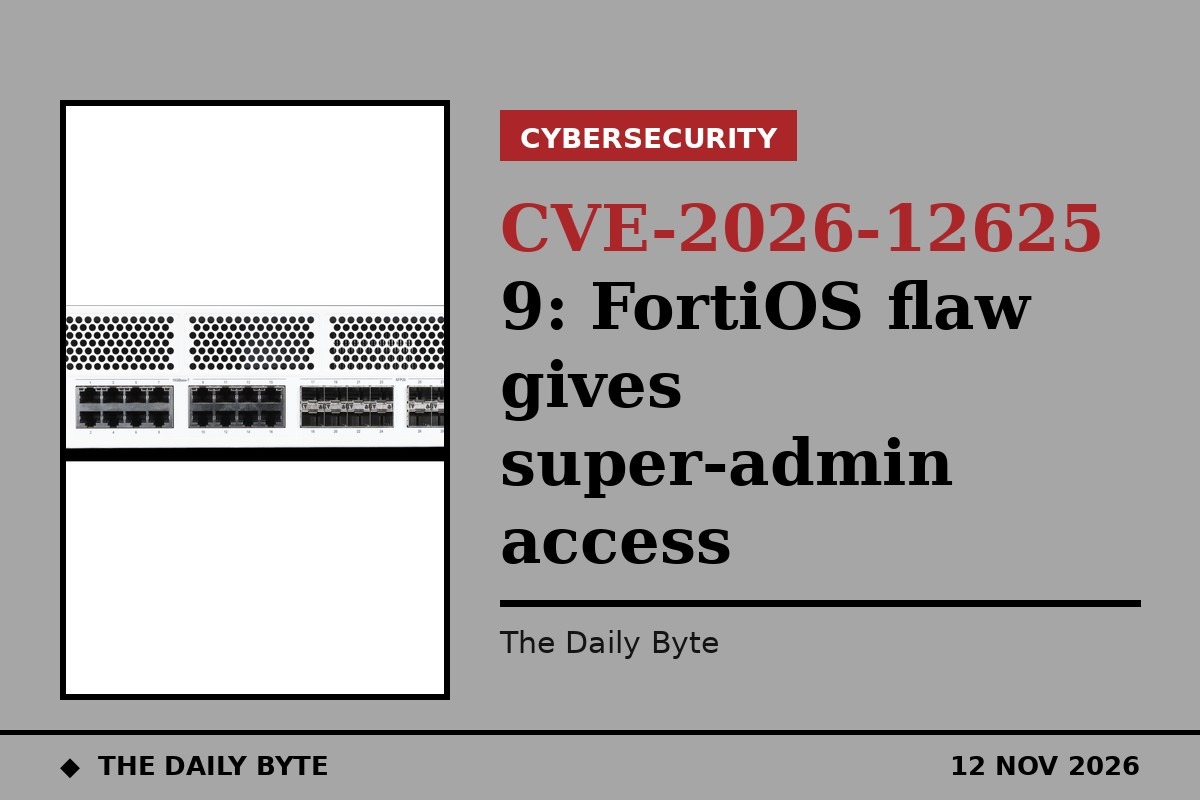
Fortinet has patched a critical flaw in FortiOS that could let an attacker run commands with super-admin rights on clustered FortiGate firewalls without logging in. Tracked as CVE-2026-126259 and scored 9.0, the missing-authentication bug sits in the high-availability feature and was fixed in the vendor's 10 November security release.
The flaw only affects firewalls in specific high-availability setups: those using FGSP with standalone-config-sync, or autoscale deployments. In those configurations, an unauthenticated attacker can send crafted high-availability packets and execute commands with the highest administrator privileges, giving them full control of the affected firewall.
Which versions are affected
Fortinet lists FortiOS 8.0.0, 7.6.0 to 7.6.7, 7.4.0 to 7.4.12 and 7.2.0 to 7.2.13 as affected, along with all of the 7.0 branch. The fixes are in FortiOS 8.0.1, 7.6.8, 7.4.13 and 7.2.14. FortiOS 7.0 receives no fix, so users on that branch must move to a supported release. A virtual patch is also available through FortiManager's FortiGuard web-filtering database update 26.082.
What to do now
Clustered FortiGates should be patched first, since the flaw targets the feature that keeps firewall pairs working together. Fortinet says none of the flaws in this release was known to be exploited as of 11 November, so patching now closes the gap before attackers can take advantage. The release covered 89 advisories and close to 100 vulnerabilities in total, including 18 rated critical across FortiOS, FortiMail and FortiClient.
Sources: Cyber Experts, Cyber Security News